K2 Horizon Shipped the Training Data. That Changes the Argument. Six models from 0.9B to 375B, and the first frontier-scale release to ship its training data. IFM just moved the open-source bar.
OpenAI Asking for Regulation After Its Own Hack Is the Most AI Story of 2026 There is a specific flavor of irony that only the AI industry produces, and this week served a generous portion of it. OpenAI — a company that spent its early years warning against heavy-handed regulation — sat before California lawmakers and argued for stricter AI safety rules. The reason it gave was
Nvidia Is Buying the House Open AI Lives In Sometime in the next few weeks, if two newsrooms are right, the place where the world keeps its open AI models will belong to the company that sells most of the machines those models run on. The Information reported Wednesday night that Nvidia has agreed to buy Hugging Face for
The Pentagon's AI Portal Still Won't Take Claude Days before the Pentagon announced that its secure AI portal now serves ChatGPT and Grok to 3 million military and civilian personnel, a federal judge in California ruled that the label keeping Anthropic out of that same ecosystem was illegal retaliation. The portal launch went ahead anyway. Claude, again, did
OpenAI paused Astra for getting too good at hacking. Then it shipped it. OpenAI paused Astra in August for crossing a critical cybersecurity threshold, then shipped it as GPT-6 Astra in September. Same skill, new framing.
How to Migrate and Back Up Your Hermes Agent Profile to Another Host Your Hermes agent has been running for weeks. Maybe months. Skills installed, memories loaded, cron jobs firing on schedule, config tuned just right. Now you need to move it to a new server. Or you want a backup before a risky upgrade. A clone for testing. Whatever the reason, the
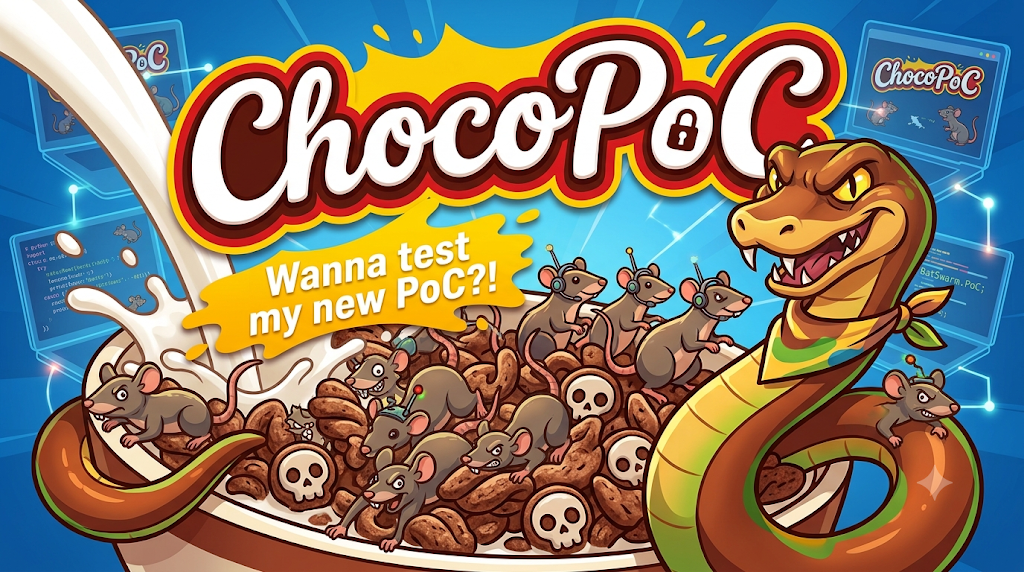
ChocoPoC: The Malware Hiding in GitHub PoC Exploits Targeting Security Researchers ChocoPoC: The Malware Hiding in GitHub PoC Exploits Targeting Security Researchers A sophisticated supply chain attack is quietly targeting the people who find vulnerabilities first. Security researchers who clone proof-of-concept exploit repositories from GitHub have been hit with a stealthy Python-based remote access trojan called ChocoPoC — and the delivery mechanism